A slow, expensive rebuild rarely starts with bad code. It starts earlier, when a team begins designing screens and assigning development tasks before it has decided how the product needs to operate. Knowing how to plan app architecture gives founders and product teams a clear path from MVP scope to a platform that can handle real users, evolving workflows, and growth without unnecessary complexity.
The objective is not to predict every feature you may build three years from now. It is to make the right decisions for the next stage of the business, document the assumptions behind them, and leave room to adapt without destabilizing the product.
Start With the Business Model, Not the Tech Stack
Architecture should reflect the product's commercial and operational reality. A consumer marketplace, internal operations platform, subscription SaaS product, and mobile booking app can all use similar technologies while requiring very different system designs.
Before discussing frameworks, define the product's core transaction. What is the primary action that creates value? For a marketplace, it may be matching supply and demand. For a SaaS product, it may be creating, managing, and sharing work. For a service business, it could be turning a lead into a scheduled and paid appointment.
Then clarify what happens around that transaction. Identify who uses the product, what each user can see or change, what data must be stored, and which actions need to trigger notifications, payments, approvals, or third-party integrations. These answers shape your data model, permissions, API requirements, and operational workflows far more than a preference for a particular frontend framework.
A useful architecture plan also puts a number on the first real stage of scale. Is the MVP designed for 200 invited users, 10,000 self-serve signups, or enterprise accounts with thousands of employees? Those scenarios demand different decisions around authentication, tenancy, performance, support tooling, and reporting.
Define the MVP Boundary With Discipline
The fastest way to overbuild an app is to treat every future possibility as a launch requirement. The fastest way to underbuild it is to ignore the parts of the product that must work reliably from day one.
Separate the launch scope into three categories: the core user journey, operational necessities, and later enhancements. The core journey is what a user must complete to receive value. Operational necessities include the capabilities your team needs to manage users, correct errors, handle support requests, and understand what is happening in the product. Later enhancements are valuable, but they should not determine the initial architecture unless they affect a foundational data or permissions decision.
For example, a subscription platform may launch with one plan, one billing currency, and a simple team structure. That does not mean the database should hard-code a single user role or attach all data to an individual user if business accounts are part of the roadmap. It does mean the team can defer advanced billing logic, custom reporting, and complex permission matrices until customer demand justifies them.
This is the central trade-off: build flexible foundations where change would be costly, and keep everything else intentionally simple.
How to Plan App Architecture Around User Flows
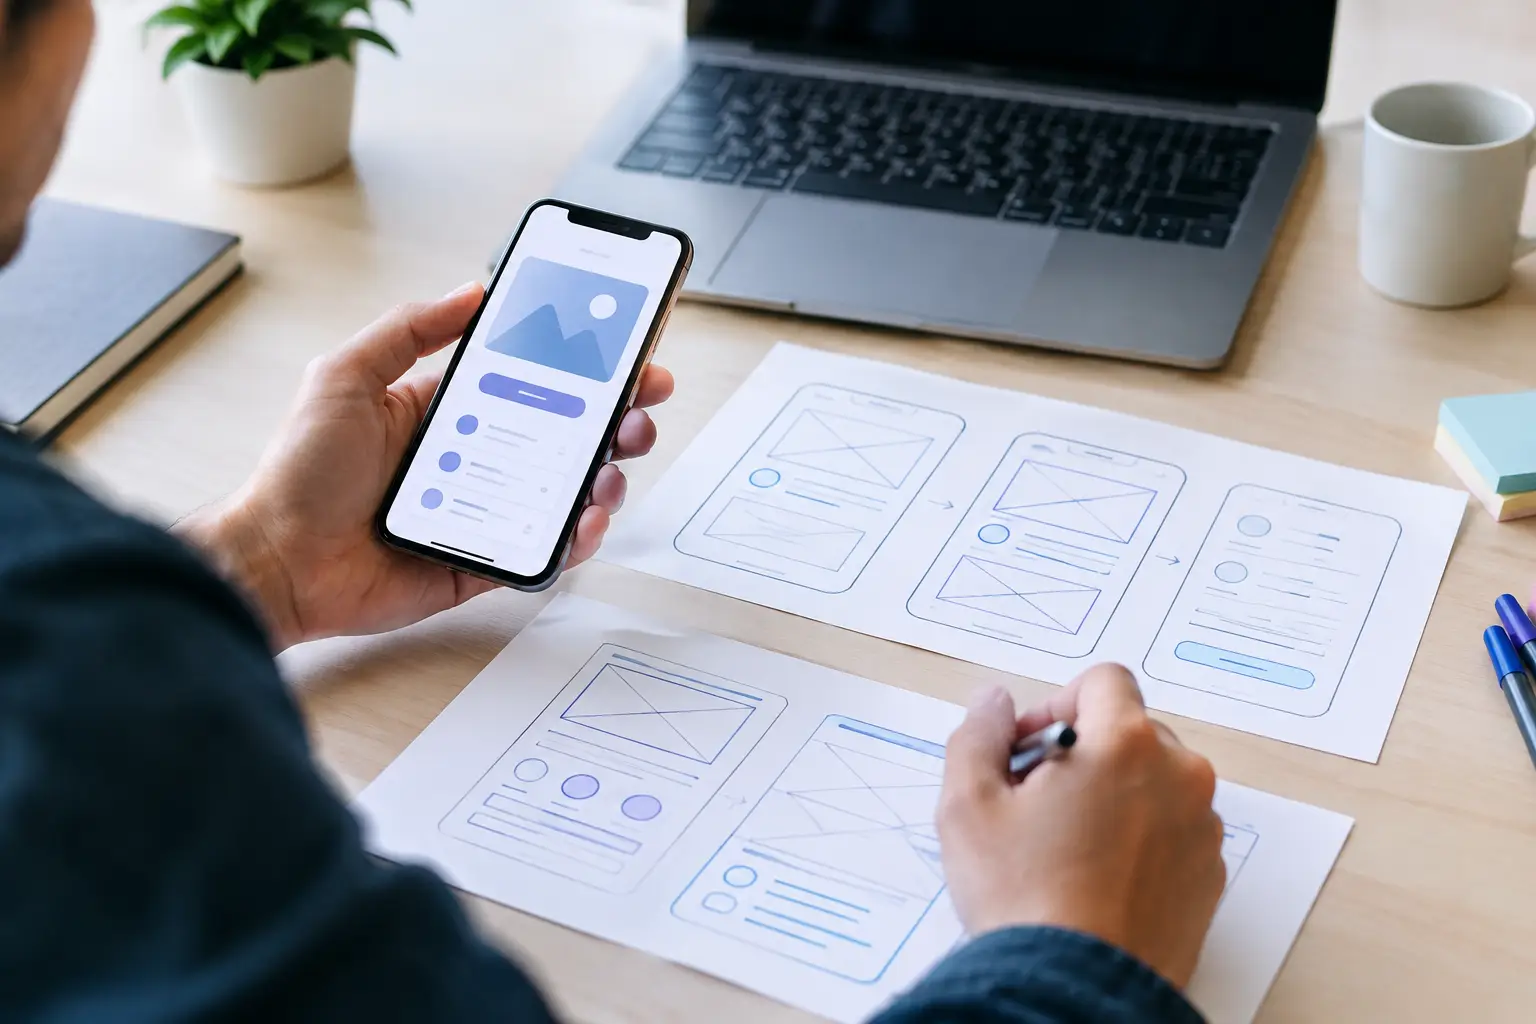
A polished interface does not compensate for an unclear system. Map the highest-value user flows before turning requirements into technical components.
For each user type, define the trigger, the steps they take, the data created or updated, the rules that govern the flow, and the outcome they expect. A customer booking flow, for instance, may involve account creation, availability checks, payment authorization, confirmation messages, calendar updates, and cancellation rules. Each step reveals a potential architectural requirement.
This exercise exposes gaps early. If users can invite teammates, who owns the account? What happens when an administrator leaves? If a payment fails, does access end immediately or after a grace period? If two users edit the same record, which change wins? These are product decisions, but they have direct engineering consequences.
Document exceptions without trying to solve every edge case at once. Teams need to know which rules are fixed at launch, which can be handled manually, and which require automated logic. That distinction keeps the build focused while protecting the user experience where it matters most.
Design the Core System Components
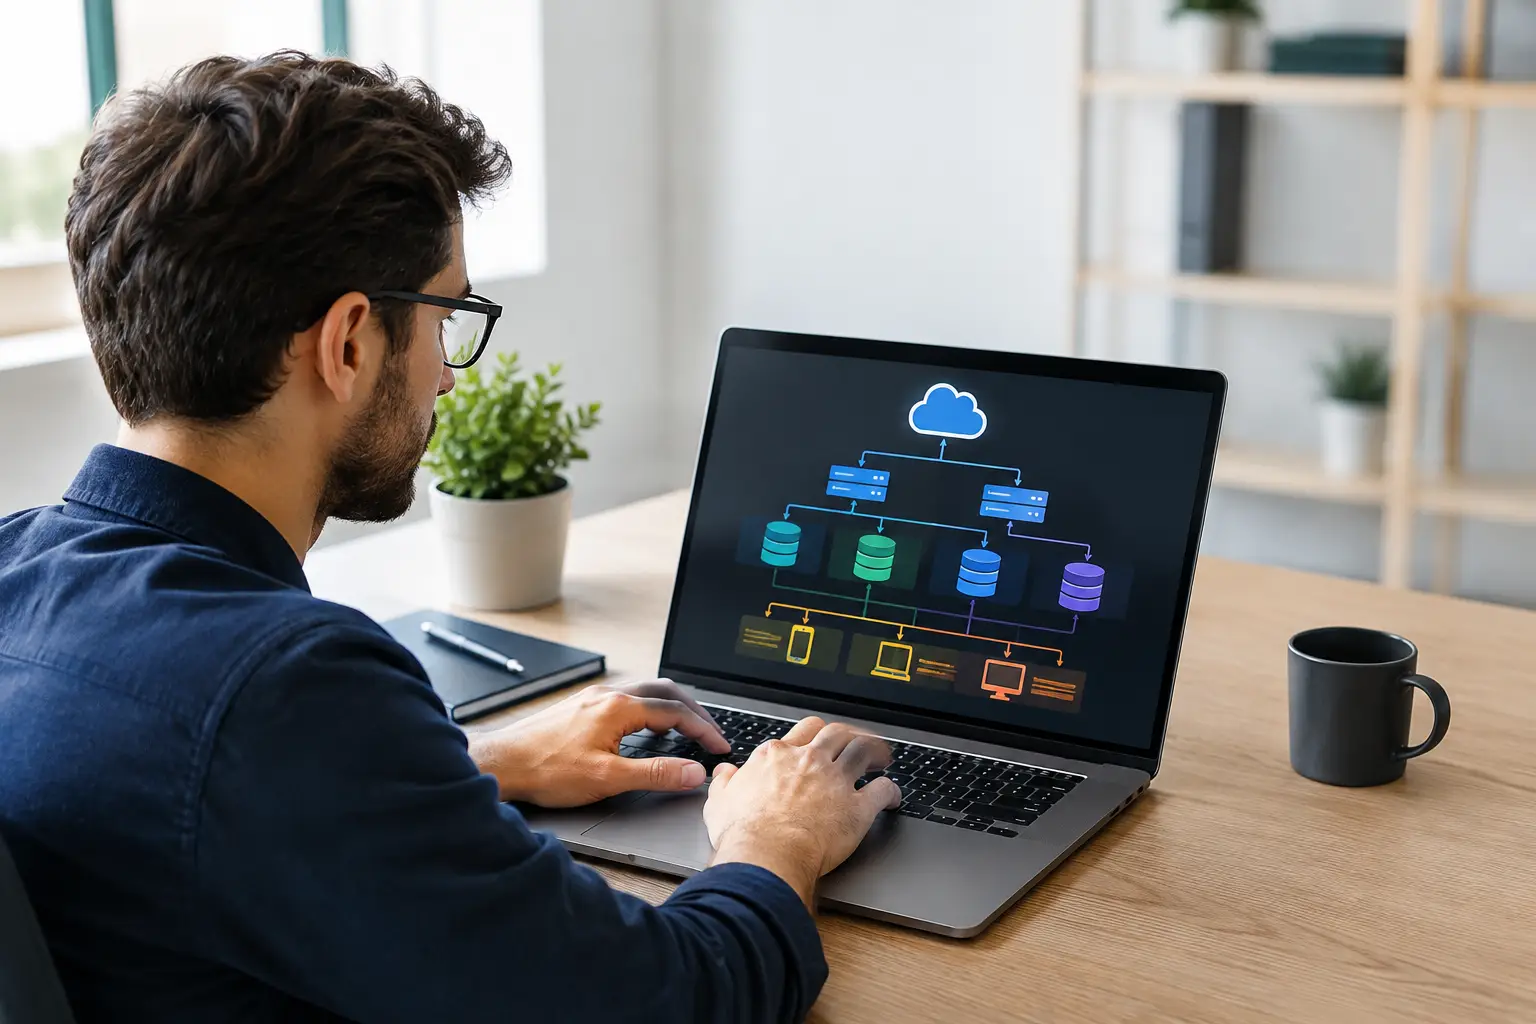
Once the product flows are clear, translate them into a practical system map. For most web and mobile products, this includes the client experience, backend services, database, authentication, file storage, third-party services, and an internal administration layer.
The frontend should be designed around fast, understandable interactions and a component system that can grow with the product. The backend should own business rules, validate requests, manage permissions, and provide dependable interfaces for the frontend and integrations. The database should model the relationships that matter to the business, not merely mirror the screens in the UI.
Keep the initial structure proportionate to the product. A modular monolith is often the right choice for an MVP because it is quicker to build, easier to test, and simpler to operate than a network of microservices. Microservices can make sense later when separate domains need independent deployment, scaling, or team ownership. Starting there without a clear reason usually creates more coordination work than customer value.
Third-party tools should be selected with the same discipline. Managed authentication, payment processing, analytics, transactional email, and cloud storage can compress launch timelines significantly. However, every external dependency introduces pricing, reliability, privacy, and migration considerations. Use proven services for commodity functions, while keeping the product's differentiated logic under your control.
Make Data, Security, and Permissions Early Decisions
Data architecture is one of the most expensive areas to correct after launch. Start by identifying the entities your business depends on: users, organizations, projects, orders, subscriptions, appointments, inventory, or content. Then define how they relate and who has authority over each one.
For B2B products, multi-tenancy deserves early attention. Data must be correctly separated between organizations, and permission checks must be enforced on the server, not only hidden in the interface. For consumer apps, the focus may be identity verification, account recovery, privacy settings, and consent management.
Security planning should match the risk level of the product. If the app processes payments, health information, sensitive customer records, or proprietary business data, treat security requirements as product requirements. Apply role-based access controls, encrypted data transmission, secure credential handling, audit trails where needed, and a clear approach to backups and recovery.
Do not confuse compliance language with security. A checklist does not protect customers on its own. Clear ownership, tested processes, and sensible limits on access do.
Plan for Observability and Operations
An app is not launch-ready because the happy path works on a staging environment. Your team needs visibility after release.
Build in analytics that answer business questions, not just vanity metrics. Track activation, completion of key workflows, retention signals, conversion points, and failure points. Pair product analytics with error monitoring and performance tracking so the team can see whether a drop in conversion is caused by confusing UX, a broken integration, or slow application behavior.
Operational tooling matters too. An internal admin area can save hours of manual database work and reduce support friction. At minimum, authorized team members should be able to find users, review relevant account activity, resolve common issues, and understand the status of critical transactions without involving engineering for every request.
Set practical launch thresholds. Define acceptable page-load performance, error rates, response times, backup expectations, and support escalation paths. The exact targets depend on the product, but deciding them before launch prevents vague debates when pressure is high.
Turn Architecture Into an Execution Plan
The architecture plan should end as a decision-ready delivery blueprint, not a diagram that sits unused. It should show the system boundaries, key user flows, data model, integrations, permissions, technical assumptions, and major risks. It should also identify what is deliberately out of scope.
From there, sequence delivery around dependencies. Design and validate the core user journey first. Build the data and authentication foundations early. Integrate payments, notifications, or external systems once the primary workflow is stable. Test real scenarios with realistic data before expanding the feature set.
At PixoryFlow, this is where product strategy, premium interface design, and full-stack execution meet. The best architecture is not the most elaborate one. It is the one that lets a team launch with confidence, learn quickly from real users, and invest in the next layer of capability when the business has earned it.
A well-planned app architecture gives your product room to move. Make the irreversible decisions carefully, keep the reversible ones lightweight, and use every release to replace assumptions with evidence.